Quiz NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator
Quiz
tosteerthetraffic.
WhichthreeconfigurationelementsmustyouconfigurebeforeFortiGatecansteertrafficaccording
toSD-WANrules?(Choosethree.)
A.Firewallpolicies
B.Securityprofiles
C.Interfaces
D.Routing
E.Trafficshaping
Guide,fortheFortiGateSD-WANenginetosuccessfullysteertrafficusingSD-WANrules,three
fundamentalconfigurationcomponentsmustbeinplace.ThisisbecausetheSD-WANrulelookup
occursonlyaftercertaininitialconditionsaremetinthepacketflow:
Interfaces(OptionC):Youmustfirstdefinethephysicalorlogicalinterfaces(suchasISPlinks,LTE,or
VPNtunnels)asSD-WANmembers.ThesemembersarethentypicallygroupedintoSD-WANZones.
Withoutdesignatedmemberinterfaces,thereisno"pool"oflinksfortheSD-WANrulestoselect
from.
Routing(OptionD):ForapackettoevenbeconsideredbytheSD-WANengine,theremustbea
matchingrouteintheForwardingInformationBase(FIB).Usually,thisisastaticroutewherethe
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-3
destinationisthenetworkyouwanttoreach,andthegatewayinterfaceissettotheSD-WANvirtual
interface(oraspecificSD-WANzone).IfthereisnoroutepointingtoSD-WAN,theFortiGatewilluse
otherroutingtableentries(likeastandardstaticroute)andbypasstheSD-WANrule-basedsteering
logicentirely.
FirewallPolicies(OptionA):InFortiOS,notrafficisallowedtopassthroughthedeviceunlessa
FirewallPolicypermitsit.Tosteertraffic,youmusthaveapolicywheretheIncomingInterfaceisthe
internalnetworkandtheOutgoingInterfaceistheSD-WANzone(orthevirtual-wan-link).TheSD-
WANruleselectionhappensduringthe"Dirty"sessionstate,whichrequiresapolicymatchto
proceedwiththesessioncreation.
Whyotheroptionsareincorrect:
SecurityProfiles(OptionB):WhilemandatoryforApplication-levelsteering(toidentifyL7
signatures),basicSD-WANsteeringbasedonIPaddresses,ports,orISDBobjectsdoesnotrequire
securityprofilestobeactive.
TrafficShaping(OptionE):Thisisanoptimizationfeatureusedtomanagebandwidthoncesteeringis
alreadydetermined;itisnotaprerequisiteforthesteeringengineitselftofunction.
Quiz
upgrades.
WhatoptionsareavailableforhandlingfutureFortiClientupgrades?
A.EnabletheEndpointUpgradefeatureontheFortiSASEportal.
B.FortiClientwillneedtobemanuallyupgraded.
C.PerformonboardingformanagedendpointuserswithanewerFortiClientversion.
D.AnewerFortiClientversionwillbeauto-upgradedondemand.
SASEcurriculum,FortiSASEhasintroducednativelifecyclemanagementforFortiClientagentsto
reducetheoperationalburdenonITteamswhopreviouslyreliedsolelyonthird-partyMDM(Mobile
DeviceManagement)orGPO(GroupPolicyObjects)foreveryupdate.
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-4
TheEndpointUpgradefeature,foundunderSystem>EndpointUpgradeintheFortiSASEportal,
allowsadministratorstoperformthefollowing:
CentralizedVersionControl:Administratorscanseewhichversionsarecurrentlydeployedandwhich
"Recommended"versionsareavailablefromFortiGuard.
ScheduledRollouts:Youcanchoosetoupgradeallendpointsorspecificendpointgroupsata
designatedtime,ensuringthatupgradesdonotdisruptbusinessoperations.
StatusMonitoring:Theportalprovidesareal-timedashboardshowingtheprogressoftheupgrade
(e.g.,Downloading,Installing,RebootPending,orSuccess).
Manualvs.Managed:WhileMDMisstillhighlyrecommendedfortheinitialonboarding(thefirst
timeFortiClientisinstalledandconnectedtotheSASEcloud),allsubsequentupgradescanbe
handlednativelybytheFortiSASEportal.
Whyotheroptionsareincorrect:
OptionB:Manualupgradesareinefficientforlarge-scaledeployments(~400usersinthisscenario)
andarenottheintended"feature-rich"solutionprovidedbyFortiSASE.
OptionC:"Onboarding"referstotheinitialsetup.Re-onboardingeverytimeaversionchanges
wouldberedundantandcounterproductive.
OptionD:Whilethesystemcanmanagetheupgrade,itisnot"auto-upgradedondemand"bythe
clientitselfwithoutadministrativeconfigurationintheportal.Theadministratormuststilldefinethe
targetversionandschedule.
Quiz
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-5
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-6
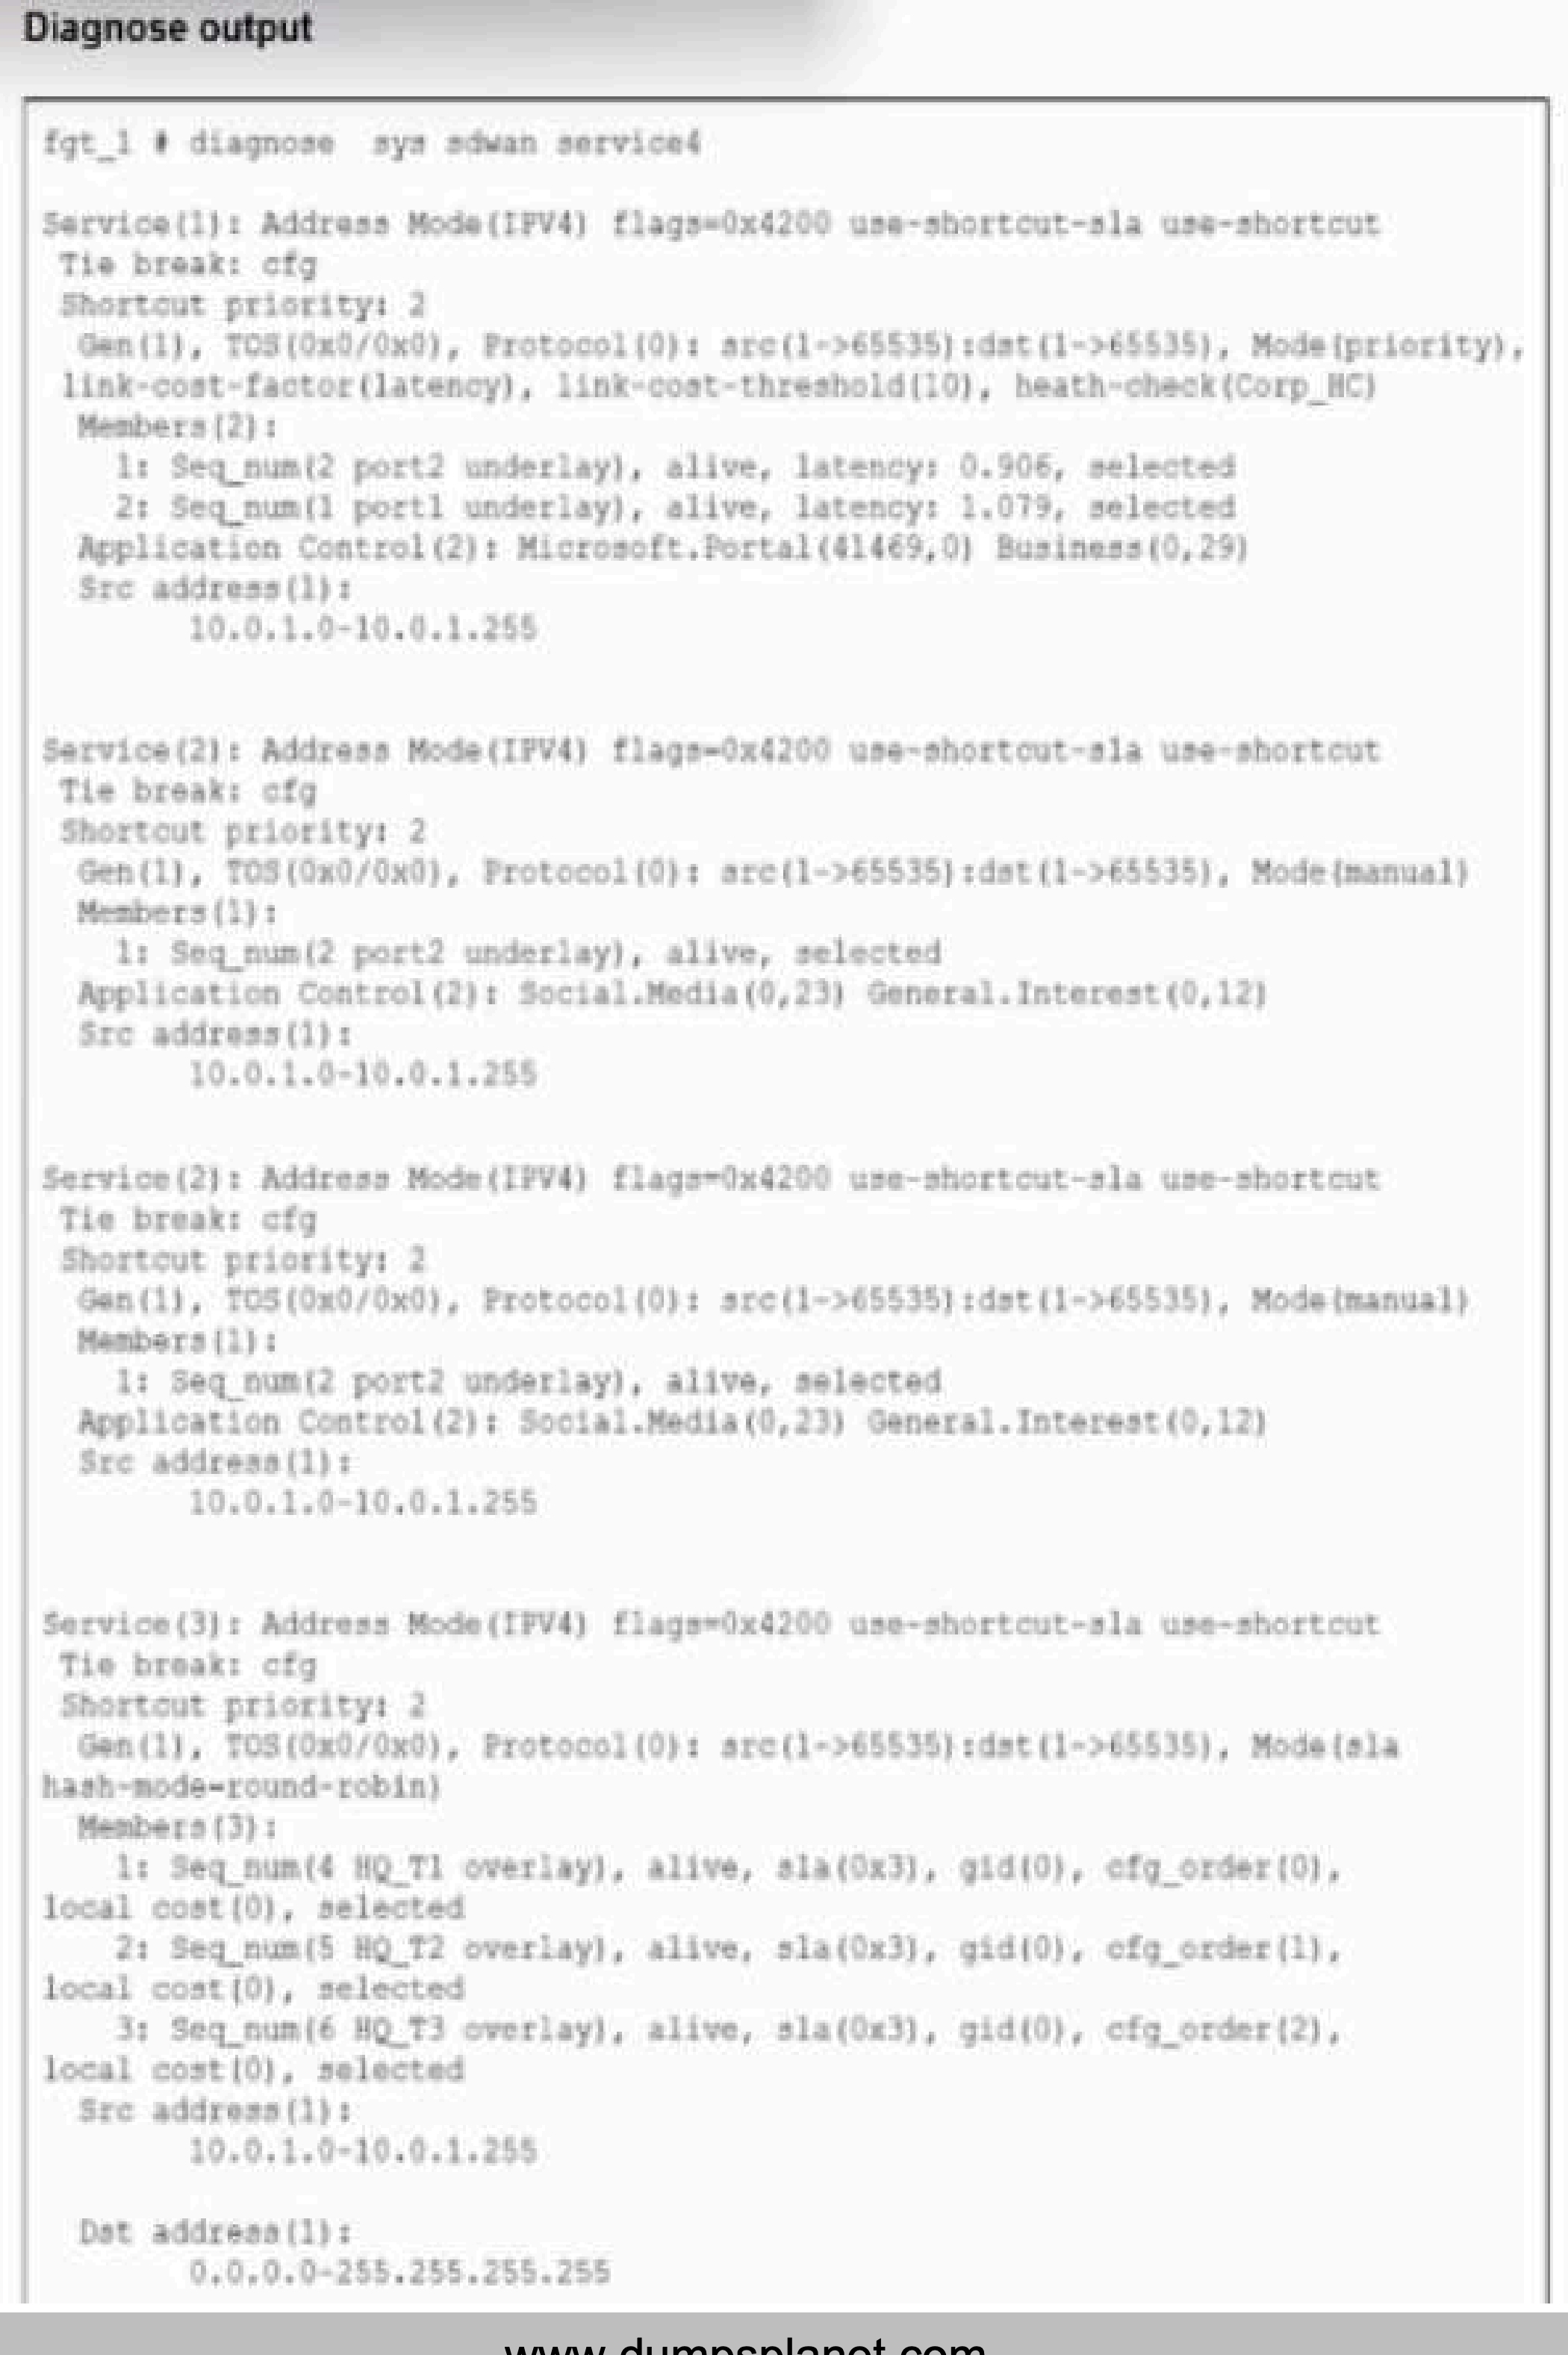
TheexhibitshowsoutputofthecommanddiagnosesyssdwanservicecollectedonaFortiGate
device.
TheadministratorwantstoknowthroughwhichinterfaceFortiGatewillsteertrafficfromlocalusers
onsubnet10.0.1.0/255.255.255.192andwithadestinationofthesocialmediaapplicationFacebook.
Basedontheexhibits,whichtwostatementsarecorrect?(Choosetwo.)
A.FortiGatesteerstrafficforsocialmediaapplicationsaccordingtotheservicerule2andsteers
trafficthroughport2.
B.ThereisnoservicedefinedfortheFacebookapplication,soFortiGateappliesservicerule3and
directsthetraffictoheadquarters.
C.WhenFortiGatecannotrecognizetheapplicationoftheflow,itloadbalancesthetrafficthrough
thetunnelsHQ_T1,HQ_T2,HQ_T3.
D.WhenFortiGatecannotrecognizetheapplicationoftheflow,itsteersthetrafficthroughthe
preferredmemberofrule3,HQ_T1.
willmatchittothecorrespondingservicerule(rule2)androuteitthroughthespecifiedinterface,
suchasport2.However,iftheapplicationisnotrecognizedduringthesessionsetup,thesystem
defaultstoloadbalancingthetrafficusingtheavailabletunnelsaccordingtothepolicyfor
unclassifiedtraffic,ensuringcontinuousconnectivitywhilewaitingforapplicationclassification."
Thisguaranteesbothperformanceandresilience.
Quiz
Whataretwoobservableimpactsofthisconfiguration?(Choosetwo.)
A.FortiGatecanoffloadthetrafficthatissubjecttopassivemonitoringtohardware.
B.FortiGatepassivelymonitorsthememberifICMPtrafficispassingthroughthemember.
C.Duringpassivemonitoring,theSLAperformancerulecannotdetectdeadmembers.
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-7
D.AfterFortiGateswitchestoactivemode,theSLAperformancerulefallsbacktopassivemonitoring
after3minutes.
E.FortiGatepassivelymonitorsthememberifTCPtrafficispassingthroughthemember.
monitoringstrategydesignedtominimizetheoverheadofsynthetictraffic(probes)while
maintaininglinkhealthvisibility.AccordingtotheFortiOS7.6AdministrationGuideandtheSD-WAN
StudyGuide,thebehaviorandimpactsareasfollows:
TCPTrafficRequirement(OptionE):PassivemonitoringreliesontheFortiGate’sabilitytoinspect
actualusertraffictocalculatehealthmetricssuchasLatency,Jitter,andPacketLoss.Specifically,it
usesTCPtraffic(byanalyzingTCPsequencenumbersandtimestampstocalculateRoundTripTime-
RTT).Ifusertrafficisflowingthroughthememberinterface,theFortiGateusesthosereal-world
sessionsforSLAcalculationsinsteadofsendingitsownprobes.
InabilitytoDetectDeadMembers(OptionC):Asignificantlimitationofpassivemonitoringisthatit
cannotdistinguishbetweena"dead"linkandan"idle"link.Ifthereisnotraffic,thepassivemonitor
hasnodatatoanalyze.Consequently,whileinpassivemode,theSD-WANenginecannotdetecta
deadmember.Tomitigatethis,"PreferPassive"includesafail-safe:ifnotrafficisdetectedfora
specificperiod(typically3minutes),theFortiGatewillautomaticallyswitchtoActivemode(sending
ICMP/TCPpings)toverifyifthelinkisactuallyalive.
Whyotheroptionsareincorrect:
OptionA:Passivemonitoringgenerallydisableshardwareoffloading(ASIC)forthemonitoredtraffic.
ThisisbecausetheCPUmustinspecteverypacketheadertocalculateperformancemetrics;ifthe
trafficwereoffloadedtotheNetworkProcessor(NP),theCPUwouldnotseethepackets,rendering
passivemonitoringimpossible.
OptionB:WhileactiveprobesoftenuseICMP,passivemonitoringisspecificallydesignedforTCP
trafficbecausetheTCPprotocol'sACKstructureallowsforaccurateRTTandlosscalculationwithout
syntheticpackets.
OptionD:The"3-minute"timerisactuallythetriggertoswitchfrompassivetoactivewhentrafficis
absent,notthefallbacktimertoreturntopassive.Thefallbacktopassivehappensassoonasvalid
TCPtrafficisdetectedagain.
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-8
AccordingtotheFortiSASE7.6AdministrationGuideandtheFCP-FortiSASE24/25Administrator
studymaterials,FortiSASEsupportsthreeprimaryexternal(remote)authenticationsourcestoverify
theidentityofremoteusers(SIAandSPAusers).Thesesourcesalloworganizationstoleveragetheir
existingidentityinfrastructureforseamlessonboardingandpolicyenforcement:
SecurityAssertionMarkupLanguage(SAML)(OptionA):Thisisthemostcommonandrecommended
methodformodernSASEdeployments.FortiSASEactsasaSAMLServiceProvider(SP)andintegrates
withIdentityProviders(IdP)suchasMicrosoftEntraID(formerlyAzureAD),Okta,or
FortiAuthenticator.ThisenablesSingleSign-On(SSO)andMulti-FactorAuthentication(MFA).
LightweightDirectoryAccessProtocol(LDAP)(OptionC):FortiSASEcanconnecttoon-premisesor
cloud-basedLDAPservers(suchasWindowsActiveDirectory).Thisallowstheadministratortomap
existingADgroupstoFortiSASEusergroupsforgranularsecuritypolicyapplication.
RemoteAuthenticationDial-inUserService(RADIUS)(OptionE):RADIUSissupportedfor
organizationsthatusecentralizedauthenticationserversortraditionalMFAsolutions(likeRSA
SecurID).FortiSASEcanqueryaRADIUSservertovalidateusercredentialsbeforegrantingaccessto
theSASEtunnel.
Whyotheroptionsareincorrect:
OpenIDConnect(OIDC)(OptionB):WhileOIDCisamodernauthenticationprotocolsimilartoSAML,
FortiSASE'sprimaryintegrationforexternalIdentityProvidersiscurrentlystandardizedonSAML2.0.
TACACS+(OptionD):TerminalAccessControllerAccess-ControlSystemPlusisprimarilyusedfor
administrativeaccess(AAA)tonetworkdevices(likeloggingintoaFortiGateCLIorFortiManager).It
isnotusedforend-userVPNorSASEauthenticationintheFortinetecosystem.
Quiz
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-9
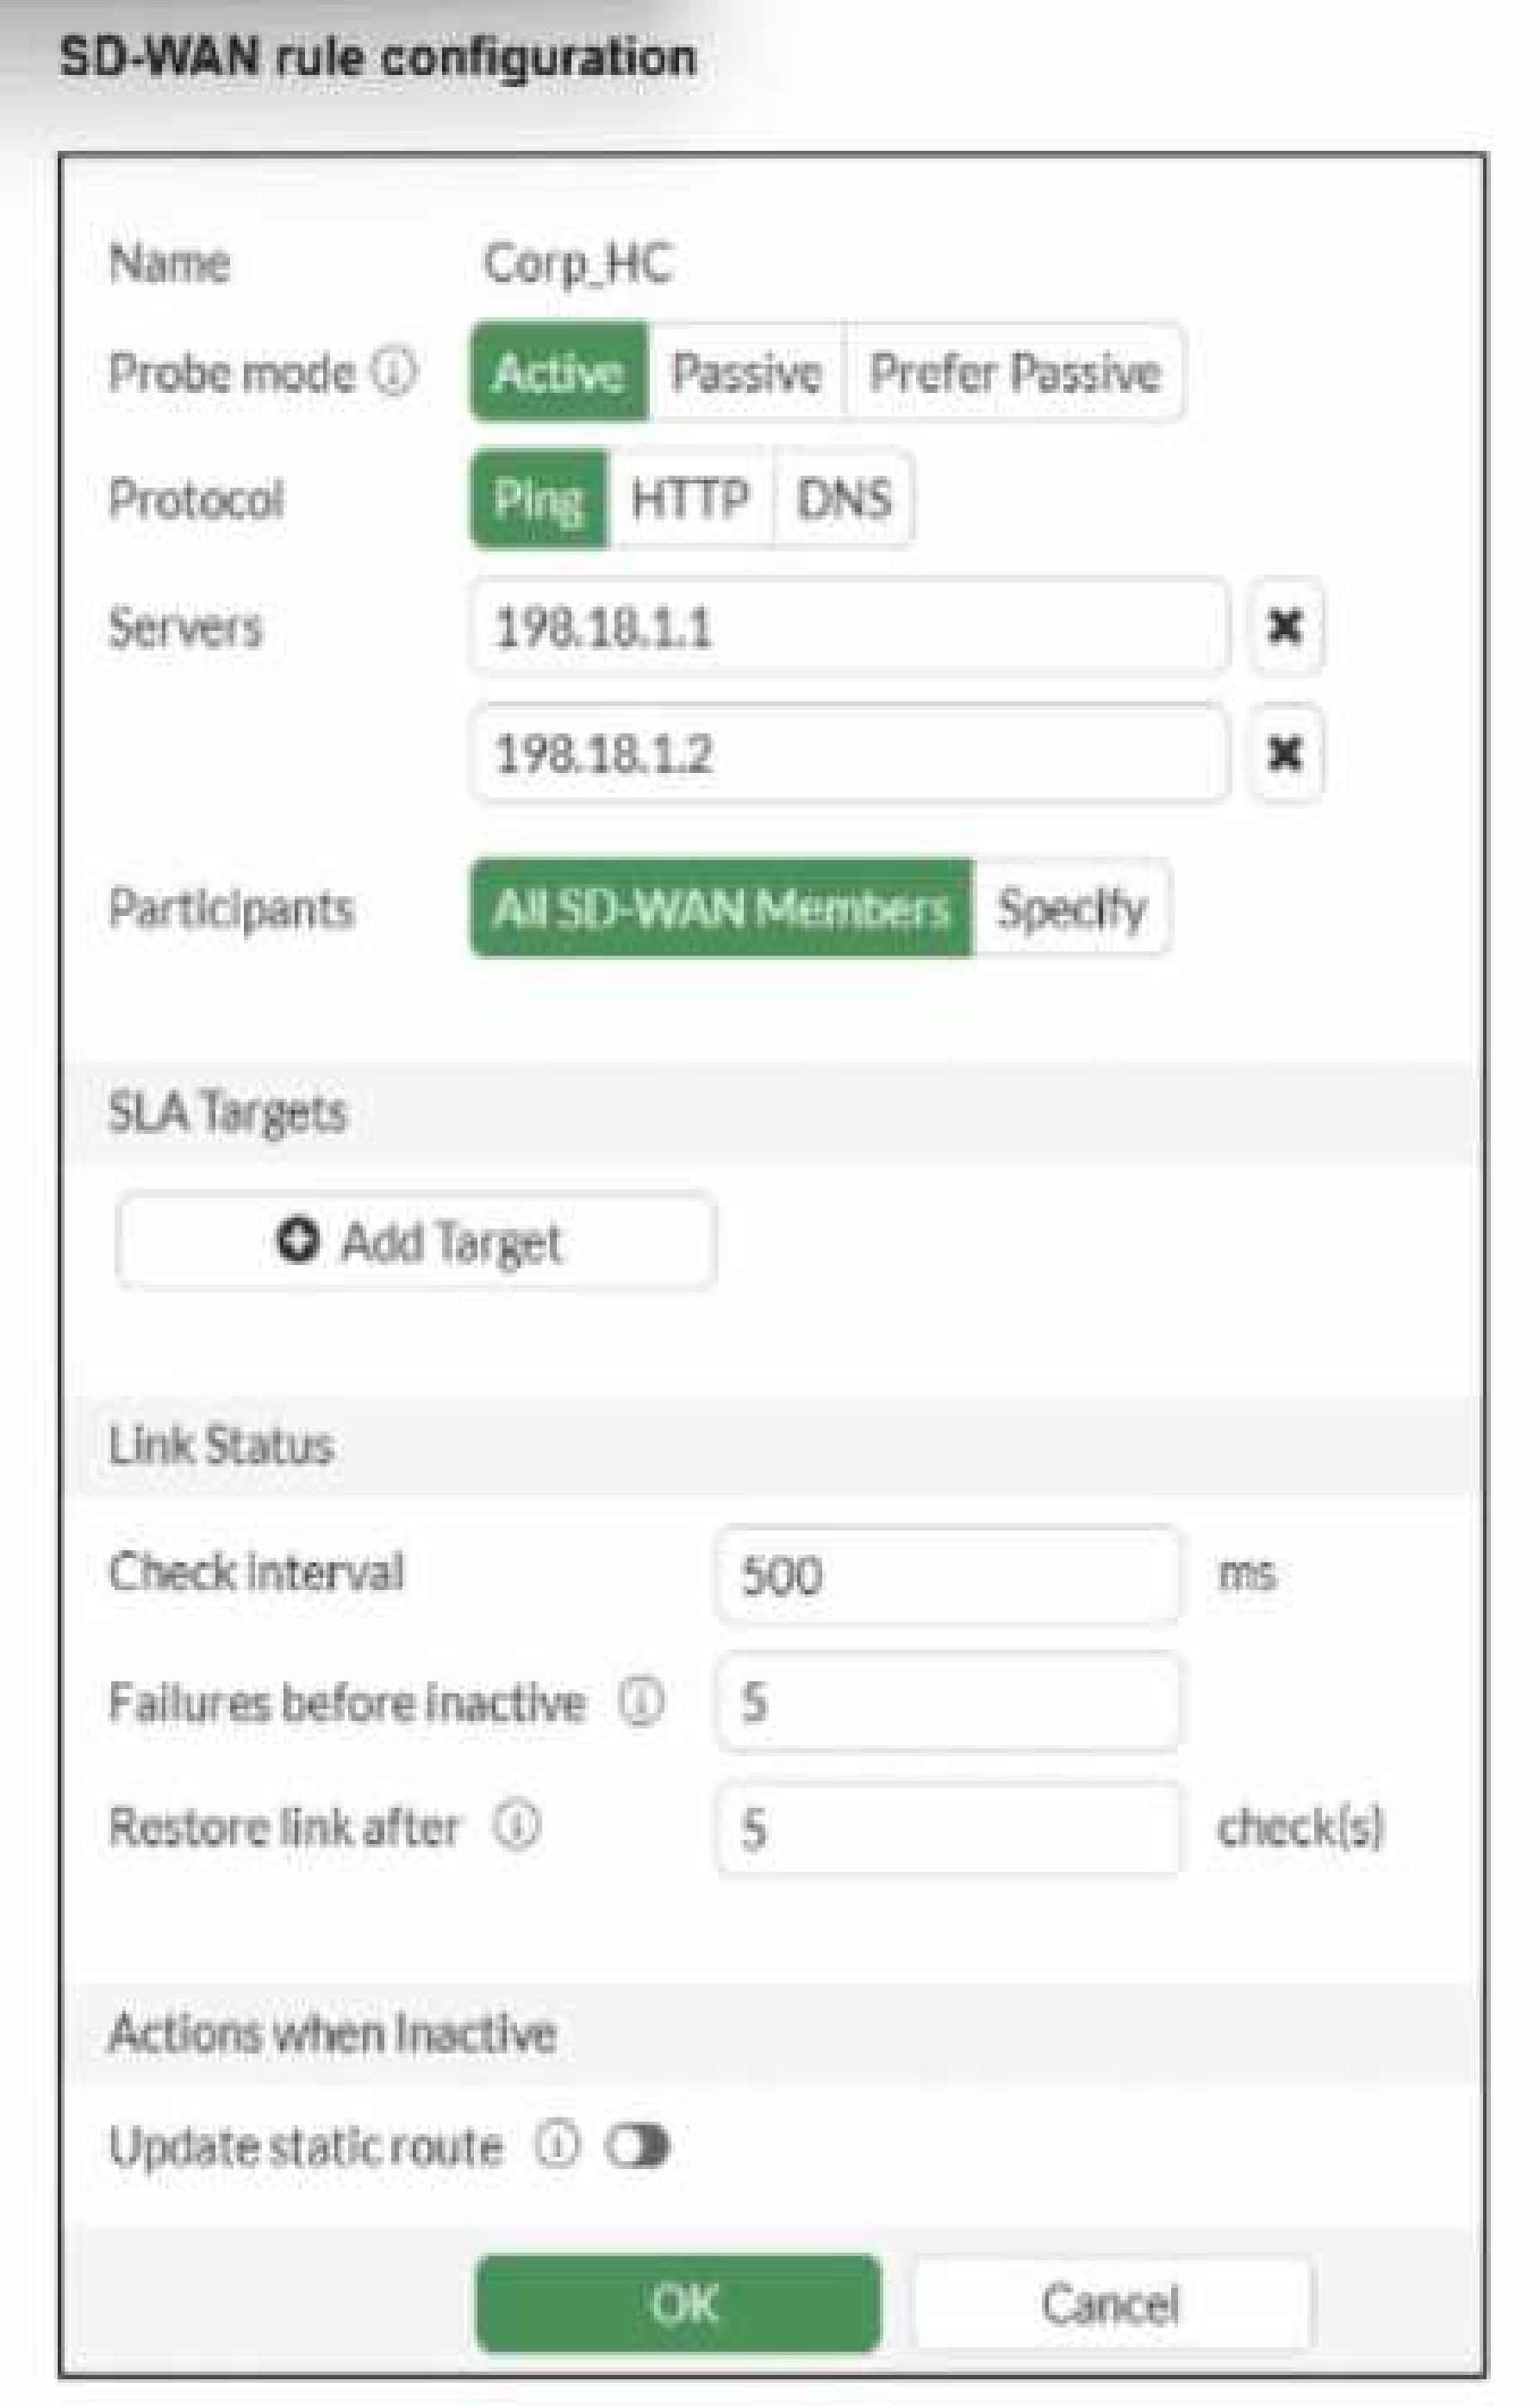
Youwanttheperformanceservice-levelagreement(SLA)tomeasurethejitterofeachmember.
Whichconfigurationchangemustyoumaketoachievethisresult?
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-10
A.Nochangeisrequired.
B.AddanSLAtargetanddefineajitterthreshold.
C.Specifytheparticipantmembers.
D.SettheprotocoltoHTTP.
noconfigurationchangeisrequiredtosimplymeasurejitter.
ImplicitMeasurement:InFortiOS,onceaPerformanceSLA(HealthCheck)isconfiguredwithan
Activeprobemode(asseenintheexhibitwithPingselected),theFortiGateautomaticallybegins
calculatingthreekeyqualitymetricsforeverymemberinterface:Latency,Jitter,andPacketLoss.
Visibility:EvenwithoutanSLATargetdefined,thesereal-timemeasurementsarevisibleintheSD-
WANMonitorandviatheCLIcommanddiagnosesysvirtual-wan-linkhealth-check<SLA_Name>.
ActiveProbes:BecausetheprobemodeissettoActiveusingthePingprotocol,theFortiGatesends
syntheticpacketsatthedefinedCheckinterval(500msintheexhibit).Itcalculatesjitterby
measuringthevariationintheround-triptime(RTT)betweentheseconsecutiveprobes.
Whyotheroptionsareincorrect:
OptionB:AddinganSLAtargetanddefiningajitterthresholdisonlynecessaryifyouwanttheSD-
WANenginetomakesteeringdecisionsbasedonthatmetric(e.g.,"removethislinkfromthepoolif
jitterexceeds50ms").Itisnotrequiredjusttomeasurethejitter.
OptionC:Whileyoucanspecifyparticipants,thecurrentsettingis"AllSD-WANMembers,"which
meansitisalreadymeasuringjitterforeverymember.
OptionD:HTTPisanalternativeprobeprotocol,butPing(ICMP)isperfectlycapableofmeasuring
jitterandisoftenpreferredforitsloweroverhead.
Quiz
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-11
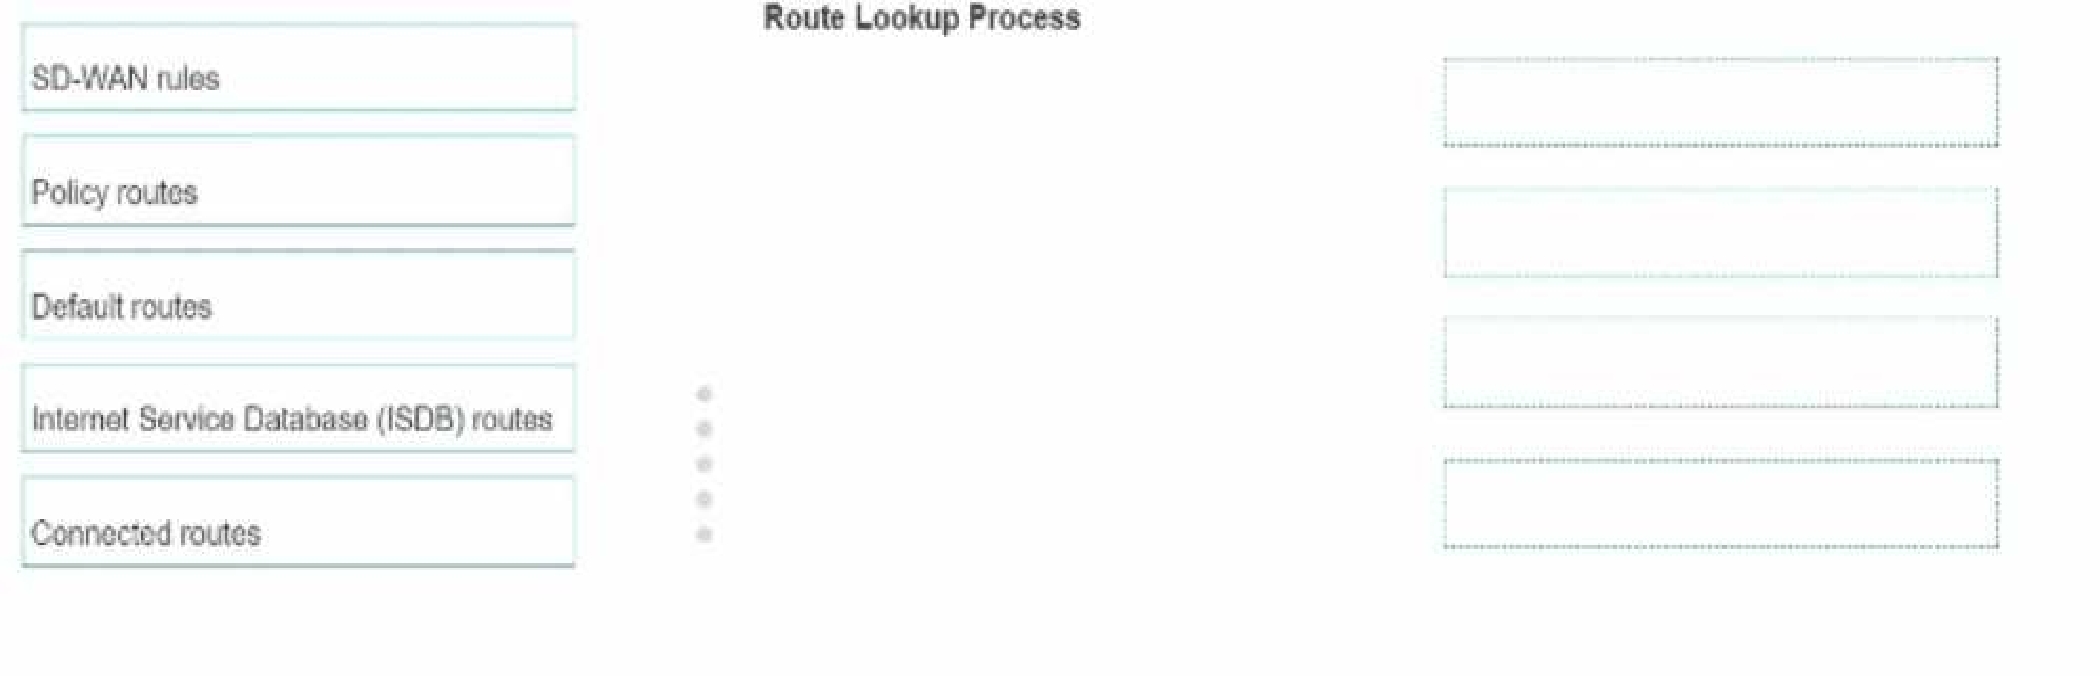
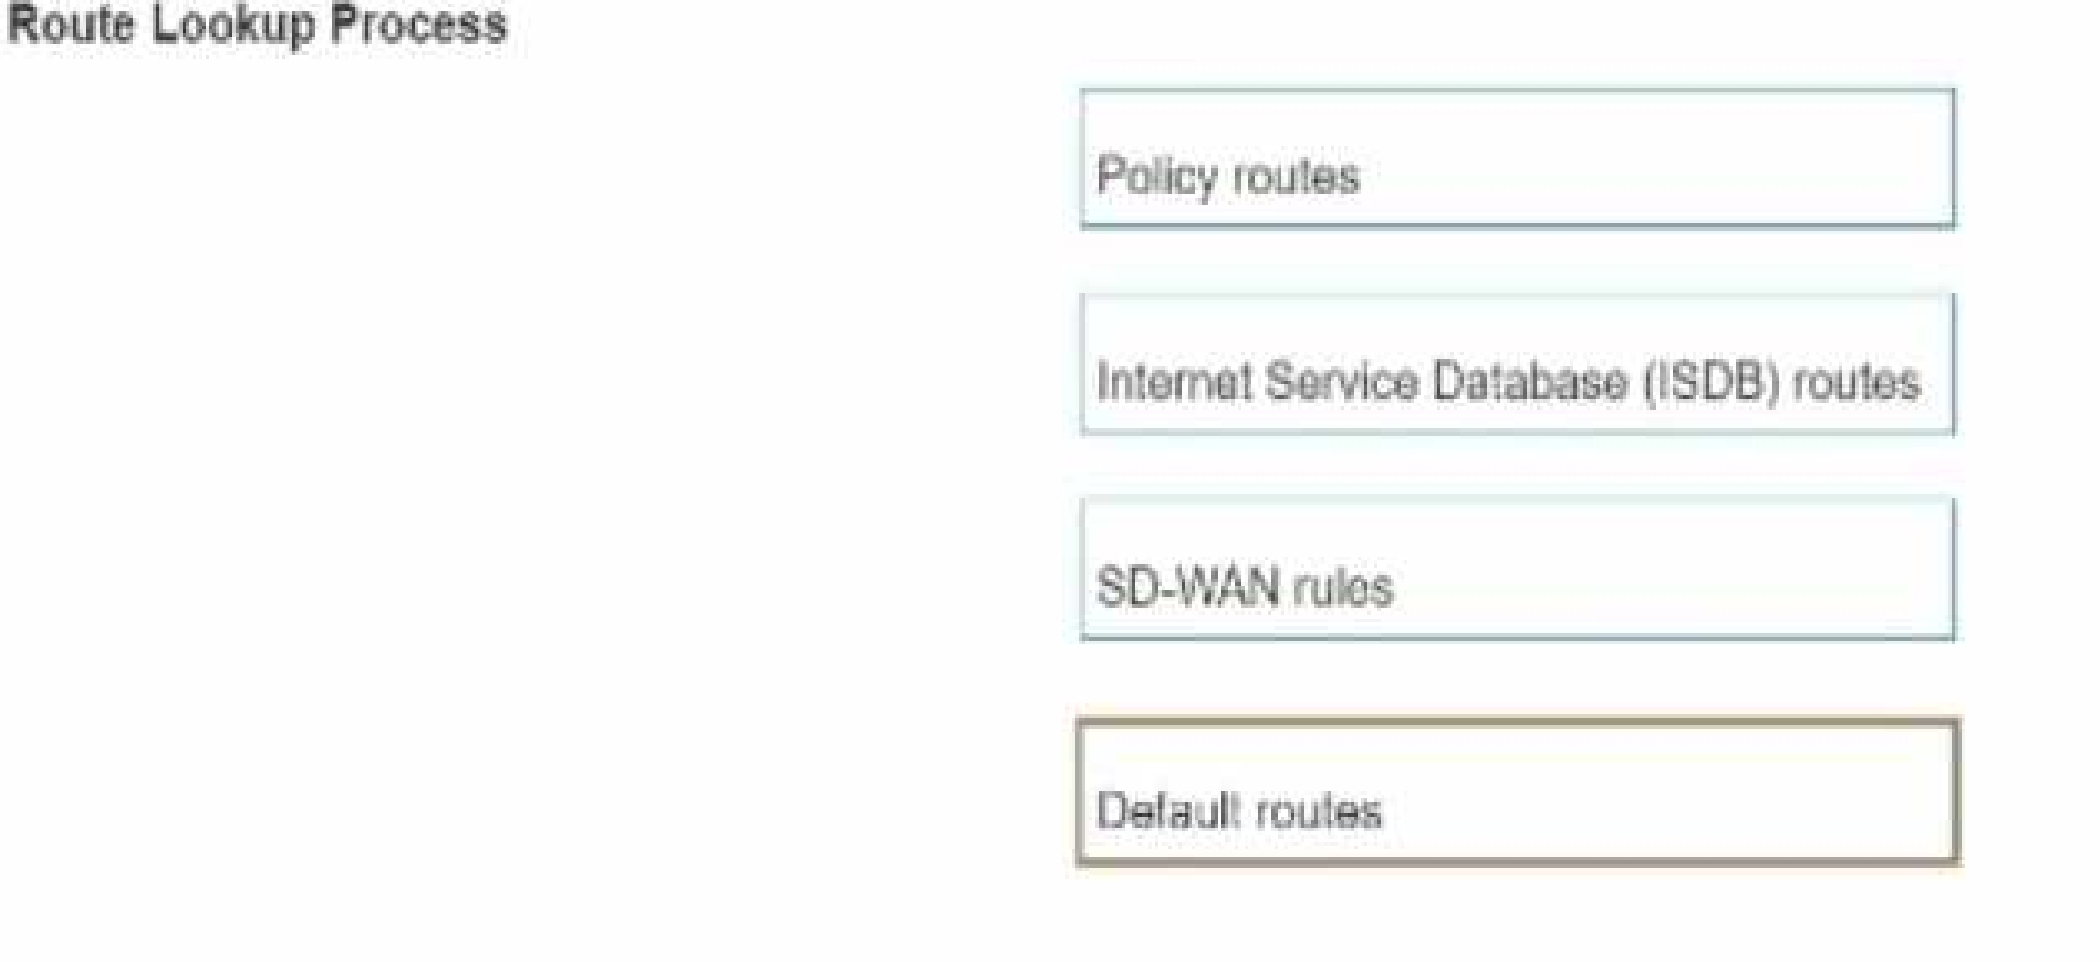
InwhichorderdoesaFortiGatedeviceconsiderthefollowingelementsshownintheleftcolumn
duringtheroutelookupprocess?
Selecttheelementintheleftcolumn,holdanddragittoablankpositioninthecolumnontheright.
Placethefourcorrectelementsinorder,placingthefirstelementinthefirstpositionatthetopof
thecolumn.Onceyouplaceanelement,youcanmoveitagainifyouwanttochangeyouranswer
beforemovingtothenextquestion.Youneedtodropfourelementsintheworkarea.
Selectanddragthescreendividertochangetheviewableareaofthesourceandworkareas.
Quiz
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-12
A.WebUsageSummaryReport
B.EndpointComplianceDeviationReport
C.VulnerabilityAssessmentReport
D.ShadowITReport
E.CyberThreatAssessment
materials,FortiSASEleveragesacloud-nativeFortiAnalyzerinstancetoprovidespecializedreports.
Thesereportsaredesignedtogiveadministratorsvisibilityintoremoteuserbehavior,endpoint
health,andcloudapplicationusage.
ThethreevalidandstandardreporttypesavailabledirectlywithintheFortiSASEportalare:
WebUsageSummaryReport(OptionA):Thisreportprovidesahigh-leveloverviewofwebactivity
acrosstheSASEdeployment.Itcategorizestrafficbywebsitecategories(e.g.,SocialMedia,
Streaming,MaliciousSites),topusersbybandwidth,andblockedrequests,helpingITteams
understandhowinternetresourcesarebeingconsumedbyremoteworkers.
VulnerabilityAssessmentReport(OptionC):SinceFortiSASEintegrateswithFortiClientandan
embeddedEMS,itcanaggregatevulnerabilityscandatafrommanagedendpoints.Thisreportlists
softwarevulnerabilitiesfoundonuserdevices(OS-levelandapplication-level),providinga"Security
Rating"orpostureassessmentthatiscriticalforZeroTrustNetworkAccess(ZTNA)enforcement.
ShadowITReport(OptionD):Leveragingthebuilt-inCASB(CloudAccessSecurityBroker)
capabilities,thisreportidentifies"unsanctioned"or"risky"SaaSapplicationsbeingusedby
employees.Ithelpsorganizationsdiscoverhiddensecurityrisksbycatalogingcloudapplicationsthat
havenotbeenexplicitlyapprovedbytheITdepartment.
Whyotheroptionsareincorrect:
EndpointComplianceDeviationReport(OptionB):WhileFortiSASEperformscompliancechecksvia
ZTNAtags,thisspecificnameisnotastandard"ReportType"templateintheportal;complianceis
typicallymonitoredviatheEndpointManagementorZTNADashboards.
CyberThreatAssessment(OptionE):TheCyberThreatAssessmentProgram(CTAP)isaspecific
Fortinetsalesandauditingtoolusedtogenerateaone-timereportonanetwork'ssecurityposture
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-13
(oftenusedforFortiGateevaluations).Itisnotanative,recurringreporttypewithintheday-to-day
FortiSASEadministrationinterface.
Quiz
ineachofthesezones.OneSD-WANmemberisnolongerusedinhealth-checkandSD-WANrules.
Thismemberistheonlymemberofitszone.Youwanttodeleteit.
WhathappensifyoudeletetheSD-WANmemberfromtheFortiGateGUI?
A.FortiGatedisplaysanerrormessage.SD-WANzonesmustcontainatleastonemember.
B.FortiGateacceptsthedeletionandremovesstaticroutesasrequired.
C.FortiGateacceptsthedeletionwithnofurtheraction.
D.FortiGateacceptsthedeletionandplacesthememberinthedefaultSD-WANzone.
ComprehensiveandDetailedExplanationwithallFortiSASEandSD-WAN7.6CoreAdministrator
curriculumdocuments:AccordingtotheSD-WAN7.6CoreAdministratorstudyguideandFortiOS7.6
AdministrationGuide,thebehaviorfordeletinganSD-WANmemberfromtheGUIwhenitisthe
onlymemberinitszoneisgovernedbythefollowingoperationallogic:
ReferenceChecks:BeforeallowingthedeletionofanySD-WANmember,FortiOSperformsa"check
fordependencies."IfaninterfaceisbeingusedinanactivePerformanceSLAoranSD-WANRule,the
GUIwilltypicallypreventthedeletionorgrayouttheoptionuntilthosereferencesareremoved.
However,thequestionspecifiesthatthismemberisnolongerusedinhealth-checksorrules.
ZoneIntegrity:Unlikesomeothernetworkobjects,anSD-WANzoneispermittedtoexistwithout
anymembers.Whenyoudeletethefinalmemberofauser-definedzonethroughtheGUI,thezone
itselfremainsintheconfigurationasanemptycontainer.
RouteManagement:WhenanSD-WANmemberisdeleted,anystaticroutesthatwerespecifically
tiedtothatinterface'smembershipintheSD-WANbundleareautomaticallyupdatedorremovedby
theFortiGatetopreventroutingloopsor"black-holing"traffic.Thisispartoftheautomatedcleanup
processhandledbytheFortiOSmanagementplane.
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-14
GUIvs.CLI:IntheGUI,theprocessisstreamlinedtoallowtheremovalofthememberinterface.
Oncethememberisdeleted,theinterfacereturnstobeinga"regular"systeminterfaceandcanbe
usedforstandardfirewallpoliciesorotherfunctions.
Whyotheroptionsareincorrect:
OptionA:Thereisnorequirementthatazonemustcontainatleastonemember;"empty"zonesare
validconfigurationobjectsinFortiOS7.6.
OptionC:Whilethedeletionisaccepted,itisnotwith"nofurtheraction"—thesystemmuststill
reconciletheroutingtableandinterfacestatus.
OptionD:FortiGatedoesnotautomaticallymovedeletedmembersintothedefaultzone(virtual-
wan-link).Oncedeleted,theinterfaceissimplynolongeranSD-WANmember.
Quiz
A.Multipletagscanbeassignedtoanendpoint,butonlyoneisusedforevaluation.
B.Multipletagscanbeassignedtoanendpointandusedforevaluation.
C.Tagsarestaticanddonotchangewithendpointstatus.
D.Onlyonetagcanbeassignedtoanendpoint.
curriculum,securityposturetags(oftenreferredtoasZTNAtags)arethefundamentalbuilding
blocksforidentity-basedandposture-basedaccesscontrol.
MultipleTagAssignment:Asingleendpointcanbeassignedmultipletagsatthesametime.For
example,anendpointmightsimultaneouslyhavethetags"OS-Windows-11","AV-Running",and
"Corporate-Domain-Joined".
EvaluationLogic:Duringthepolicyevaluationprocess(forbothSIAandSPA),FortiSASEorthe
FortiGatehubconsidersalltagsassignedtotheendpoint.Securitypoliciescanbeconfiguredtouse
thesetagsassourcecriteria.Ifanadministratordefinesapolicythatrequiresboth"AV-Running"and
"Corporate-Domain-Joined,"thesystemevaluatesbothtagstodecidewhethertopermitthetraffic.
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-15
DynamicNature:ContrarytoOptionC,thesetagsarehighlydynamic.Theyareautomaticallyapplied
orremovedinreal-timebasedonthetelemetrydatasentbytheFortiClienttotheSASEcloud.Ifa
userdisablestheirantivirus,the"AV-Running"tagisremovedimmediately,andtheendpoint's
accessisrevokedbythenextpolicyevaluation.
Scalability:Whilethesystemsupportsmanytags,documentationrecommendsabaselineofcustom
tagsforoptimalperformance,thoughitconfirmsthatmultipletagsarestandardforreflectinga
comprehensivesecurityposture.
Whyotheroptionsareincorrect:
OptionA:Thisisincorrectbecausethesystemdoesnotpickjustonetag;itevaluatesthecollection
oftagsagainstthepolicy'srequirements(e.g.,matchinganyormatchingall).
OptionC:Thisisincorrectbecausetagsaredynamicandchangeassoonastheendpoint'sstatus(like
vulnerabilitycountorsoftwarepresence)changes.
OptionD:ThisisincorrectbecausethearchitecturaladvantageofZTNAistheabilitytolayermultiple
security"checks"(tags)forasingleuser.
Quiz
A.Toenableordisableuserauthenticationforexternalnetworkaccess.
B.Todefinedifferenttrafficroutingrulesforon-premisesandcloud-basedresources.
C.Todetermineifanendpointisconnectingfromatrustednetworkoruntrustedlocation.
D.Toconfiguredifferentaccesspoliciesforusersbasedontheirgeographicallocation.
materials,theOn-netdetectionrulesettingisacriticalcomponentfordeterminingthe"truststatus"
ofanendpoint'sphysicallocation.
EndpointLocationVerification:On-netrulesetsareusedtodetermineifFortiSASEconsidersan
endpointtobeon-net(trusted)oroff-net(untrusted).Anendpointisconsideredon-netwhenitis
physicallylocatedwithinthecorporatenetwork,whichisassumedtoalreadyhaveon-premises
securitymeasures(likeaFortiGateNGFW).
[http://www.justcerts.com](http://www.justcerts.com)
Questions&AnswersPDF P-16
OperationalImpact:Whenanendpointisdetectedason-net,FortiSASEcanbeconfiguredtoexempt
theendpointfromautomaticallyestablishingaVPNtunneltotheSASEcloud.Thisoptimization
preventsredundantsecurityinspectionandconservesSASEbandwidthsincetheuserisalready
protectedbythelocalcorporatefirewall.
DetectionMethods:Toclassifyanendpointason-net,administratorsconfigurerulesetsthatlookfor
specificenvironmentalmarkers,suchas:
KnownPublic(WAN)IP:Iftheendpoint'spublicIPmatchesthecorporateheadquarters'egressIP.
DHCPServer:IftheendpointreceivesanIPfromaspecificcorporateDHCPserver.
DNSServer/Subnet:MatchinginternalDNSinfrastructureorspecificinternalIPranges.
DynamicPolicyApplication:Byaccuratelydeterminingifanendpointisonoroff-net,FortiSASE
ensuresthattheFortiClientagentonlyinitiatesitssecureinternetaccess(SIA)tunnelwhentheuser
isinanuntrustedlocation(e.g.,ahomenetworkorpublicWi-Fi).
Whyotheroptionsareincorrect:
OptionA:Userauthenticationisaseparateprocessandisnotcontrolledbytheon/off-netdetection
rules,whichfocusonthenetworkenvironmentratherthanusercredentials.
OptionB:Whileon-netstatusaffectshowtrafficisrouted(VPNvs.local),theserulesspecifically
determinethestatusitselfratherthandefiningtheroutingtablesforprivatevs.cloudresources.
OptionD:Geographicallocation(Geo-location)isadifferentfilteringcriterionoftenusedinfirewall
policies;on-netdetectionisspecificallyabouttheproximitytothetrustedcorporateperimeter.
NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Practice test unlocks all online simulator questions
Thank you for choosing the free version of the NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator practice test! Further deepen your knowledge on Fortinet Simulator; by unlocking the full version of our NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Simulator you will be able to take tests with over 44 constantly updated questions and easily pass your exam. 98% of people pass the exam in the first attempt after preparing with our 44 questions.
BUY NOWWhat to expect from our NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator practice tests and how to prepare for any exam?
The NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Simulator Practice Tests are part of the Fortinet Database and are the best way to prepare for any NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator exam. The NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator practice tests consist of 44 questions and are written by experts to help you and prepare you to pass the exam on the first attempt. The NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator database includes questions from previous and other exams, which means you will be able to practice simulating past and future questions. Preparation with NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Simulator will also give you an idea of the time it will take to complete each section of the NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator practice test . It is important to note that the NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Simulator does not replace the classic NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator study guides; however, the Simulator provides valuable insights into what to expect and how much work needs to be done to prepare for the NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator exam.
BUY NOWNSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Practice test therefore represents an excellent tool to prepare for the actual exam together with our Fortinet practice test . Our NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Simulator will help you assess your level of preparation and understand your strengths and weaknesses. Below you can read all the quizzes you will find in our NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Simulator and how our unique NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Database made up of real questions:
Info quiz:
- Quiz name:NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator
- Total number of questions:44
- Number of questions for the test:50
- Pass score:80%
You can prepare for the NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator exams with our mobile app. It is very easy to use and even works offline in case of network failure, with all the functions you need to study and practice with our NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Simulator.
Use our Mobile App, available for both Android and iOS devices, with our NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Simulator . You can use it anywhere and always remember that our mobile app is free and available on all stores.
Our Mobile App contains all NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator practice tests which consist of 44 questions and also provide study material to pass the final NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator exam with guaranteed success. Our NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator database contain hundreds of questions and Fortinet Tests related to NSE5_SSE_AD-7.6: Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Exam. This way you can practice anywhere you want, even offline without the internet.
BUY NOW